CVE-2026-90843
גבוהה 8.3
תיאור (מקור, אנגלית)
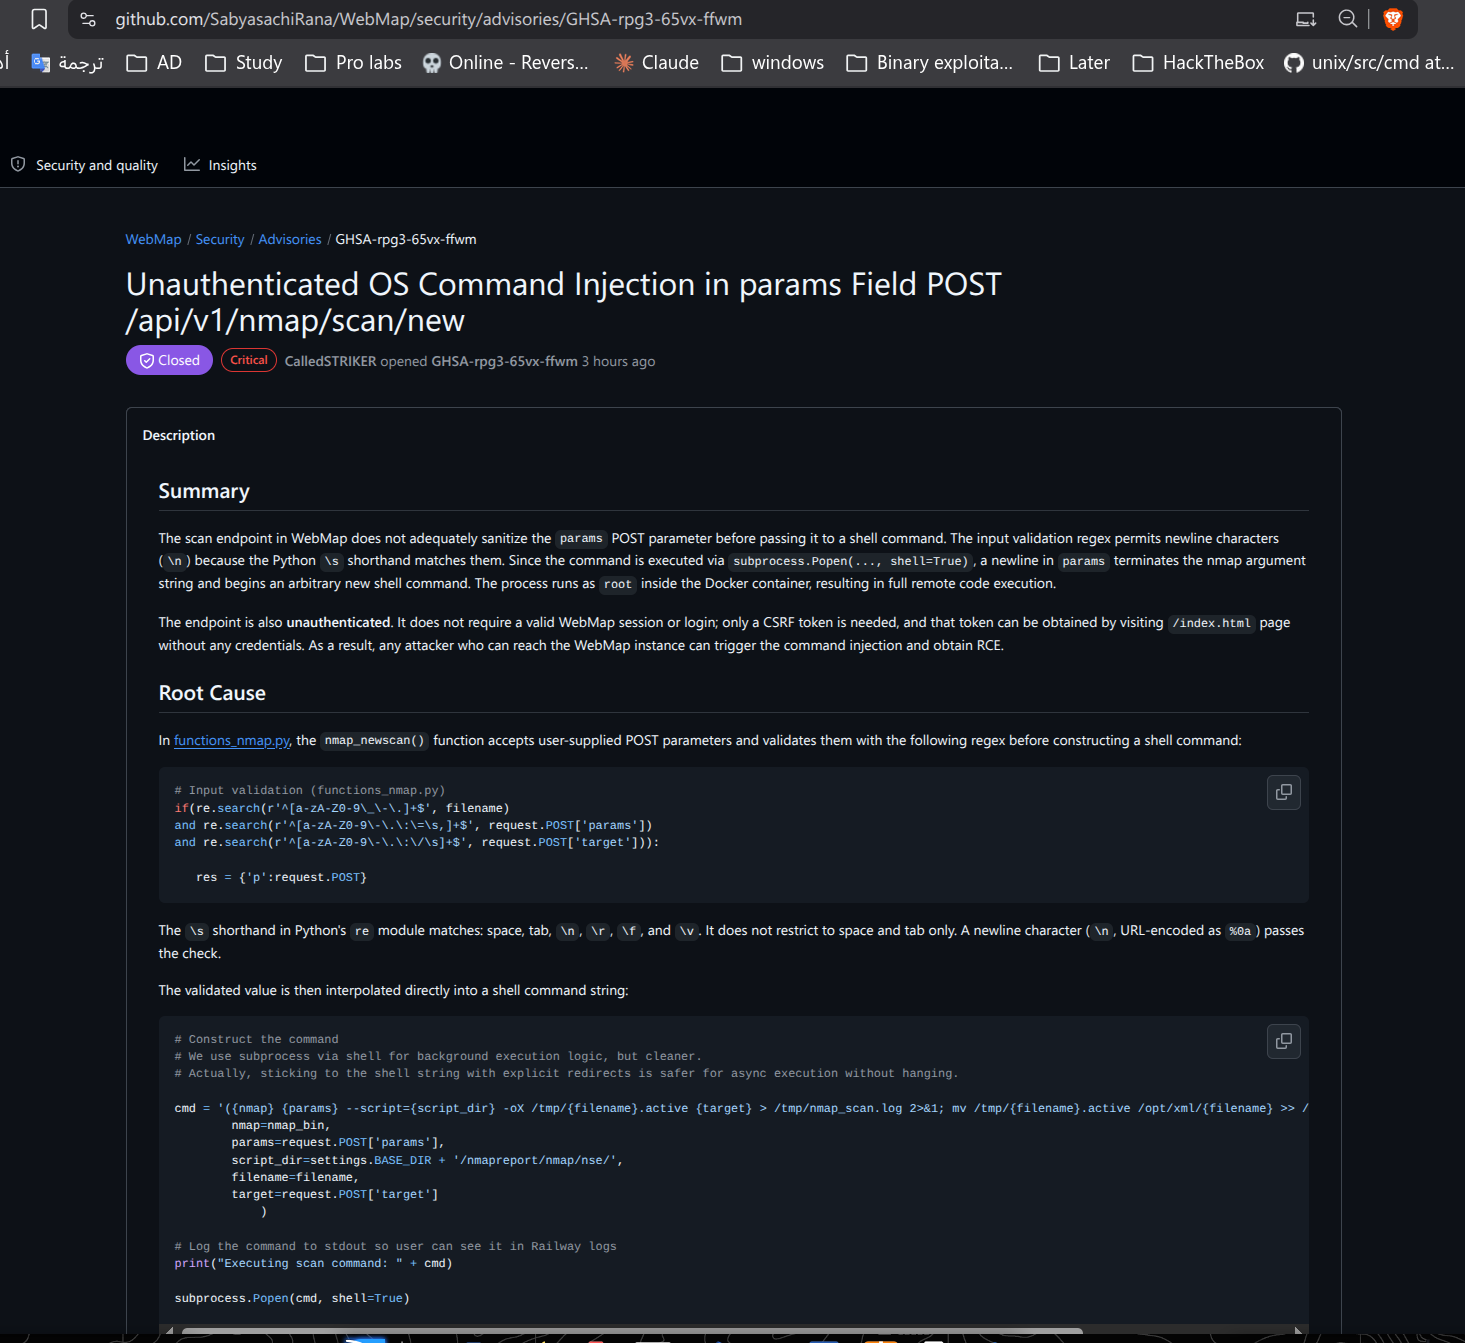
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
מדדים
- CVSS 3.1
-
8.3 (HIGH)
מקור הציון: CNA
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:L - CVSS 4.0
-
5.5 (MEDIUM)
מקור הציון: CNA
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:L/SC:L/SI:L/SA:L/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X - EPSS — סבירות ניצול
- 2% (אחוזון 100) נכון ל-28/9/2026
- CWE
- CWE-77, CWE-78
קישורים
- https://calledstriker.gitbook.io/blog/security-research/webmap
- https://github.com/SabyasachiRana/WebMap/
- https://github.com/SabyasachiRana/WebMap/commit/3d52f65803a2716bff14d938352c6f…
- https://raw.githubusercontent.com/CalledSTRIKER/CalledSTRIKER-gitbook/refs/hea…
- https://vuldb.com/cve/CVE-2026-90843
- https://vuldb.com/submit/925586
- https://vuldb.com/vuln/403395
- https://vuldb.com/vuln/403395/cti