CVE-2026-8221
נמוכה 2.4
תיאור (מקור, אנגלית)
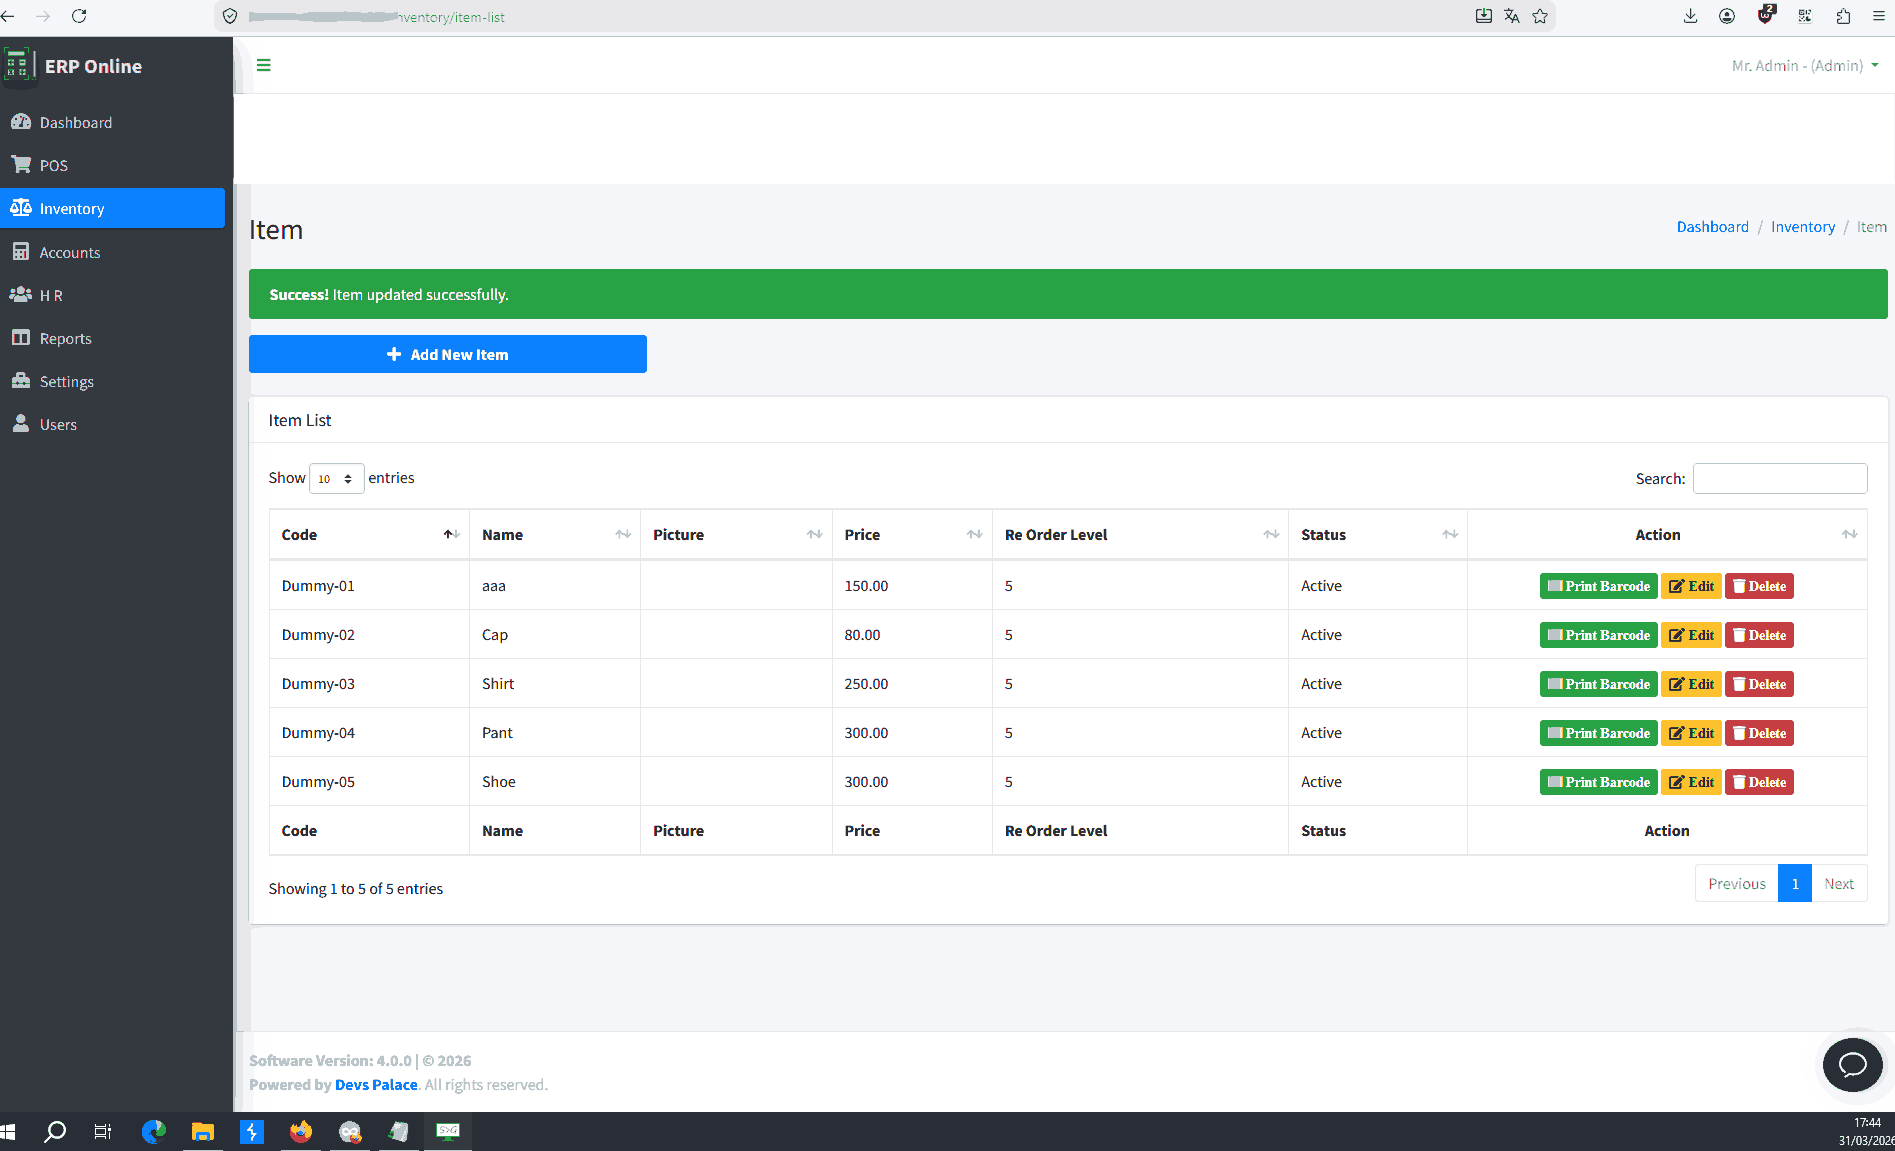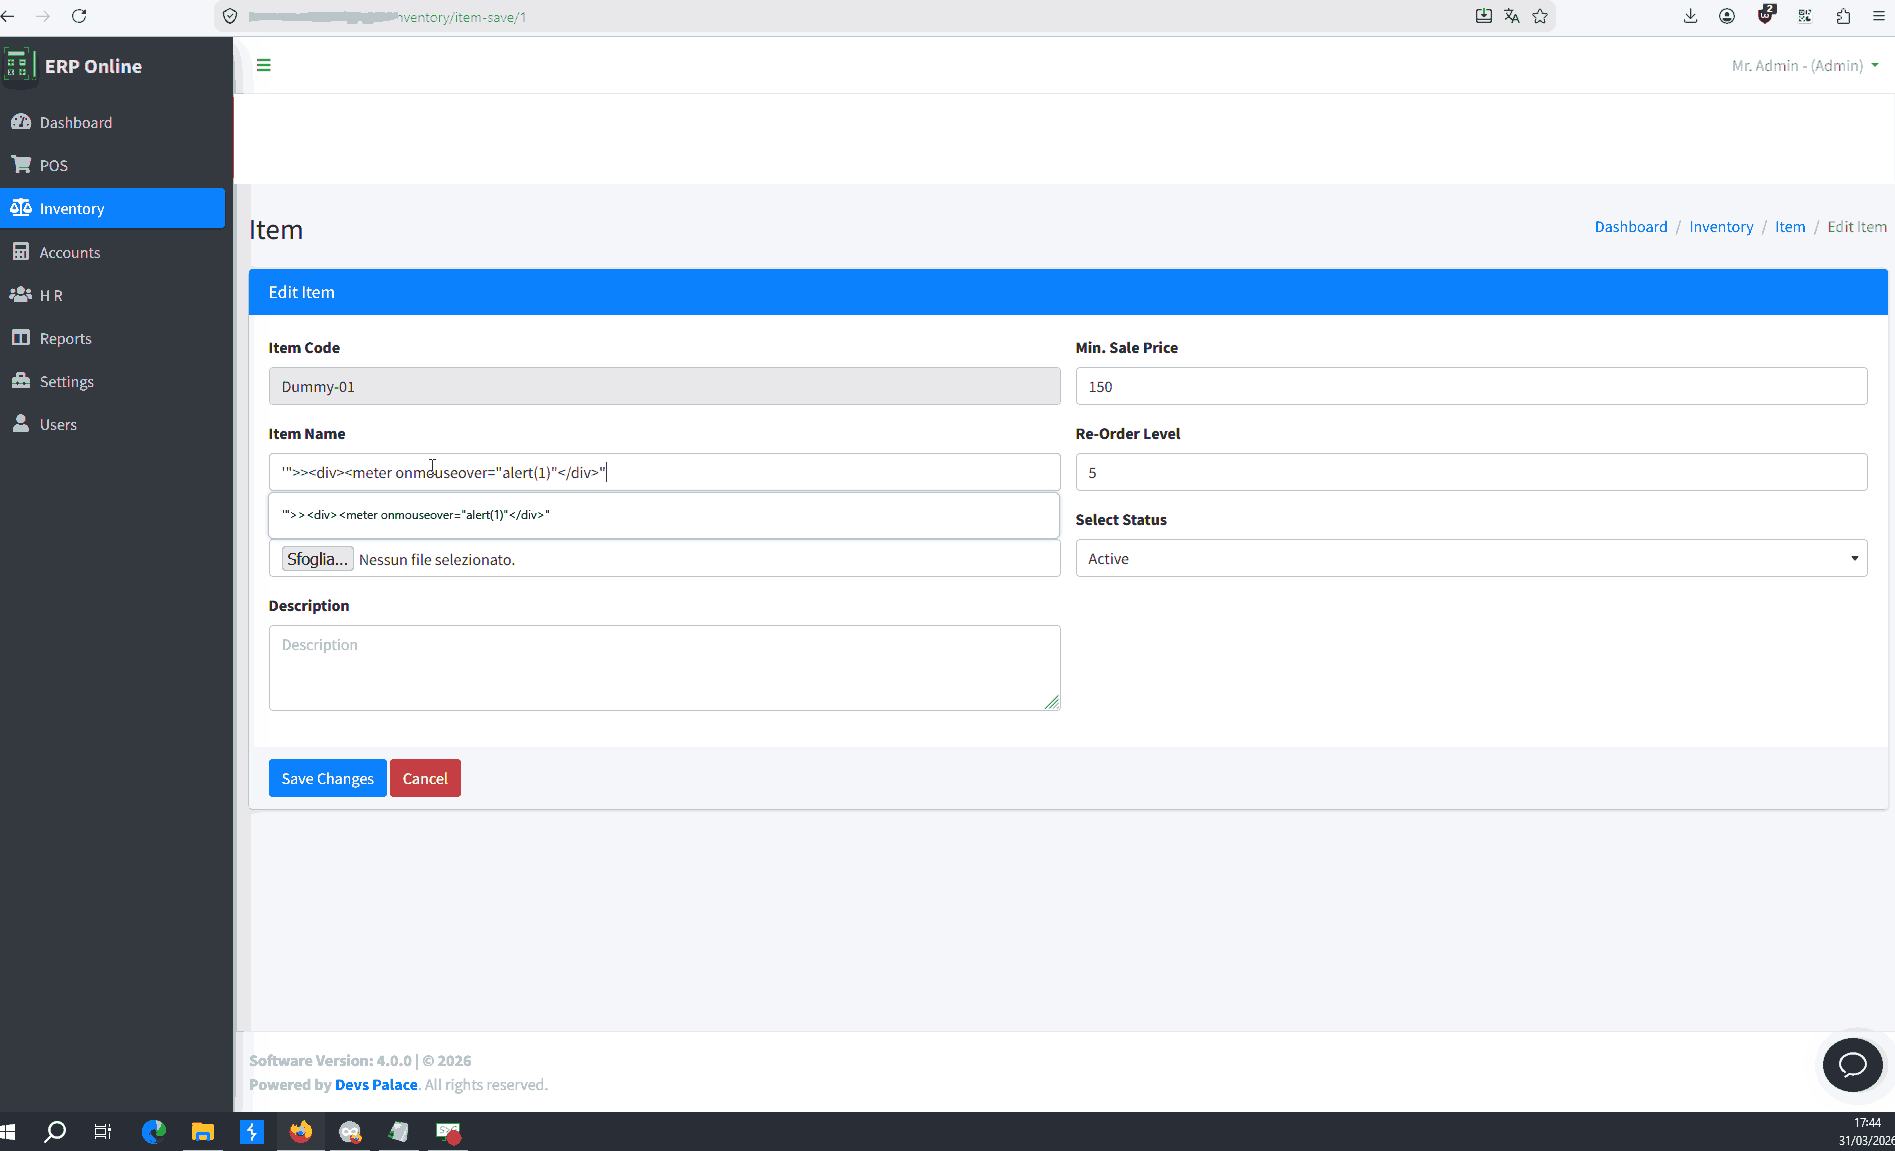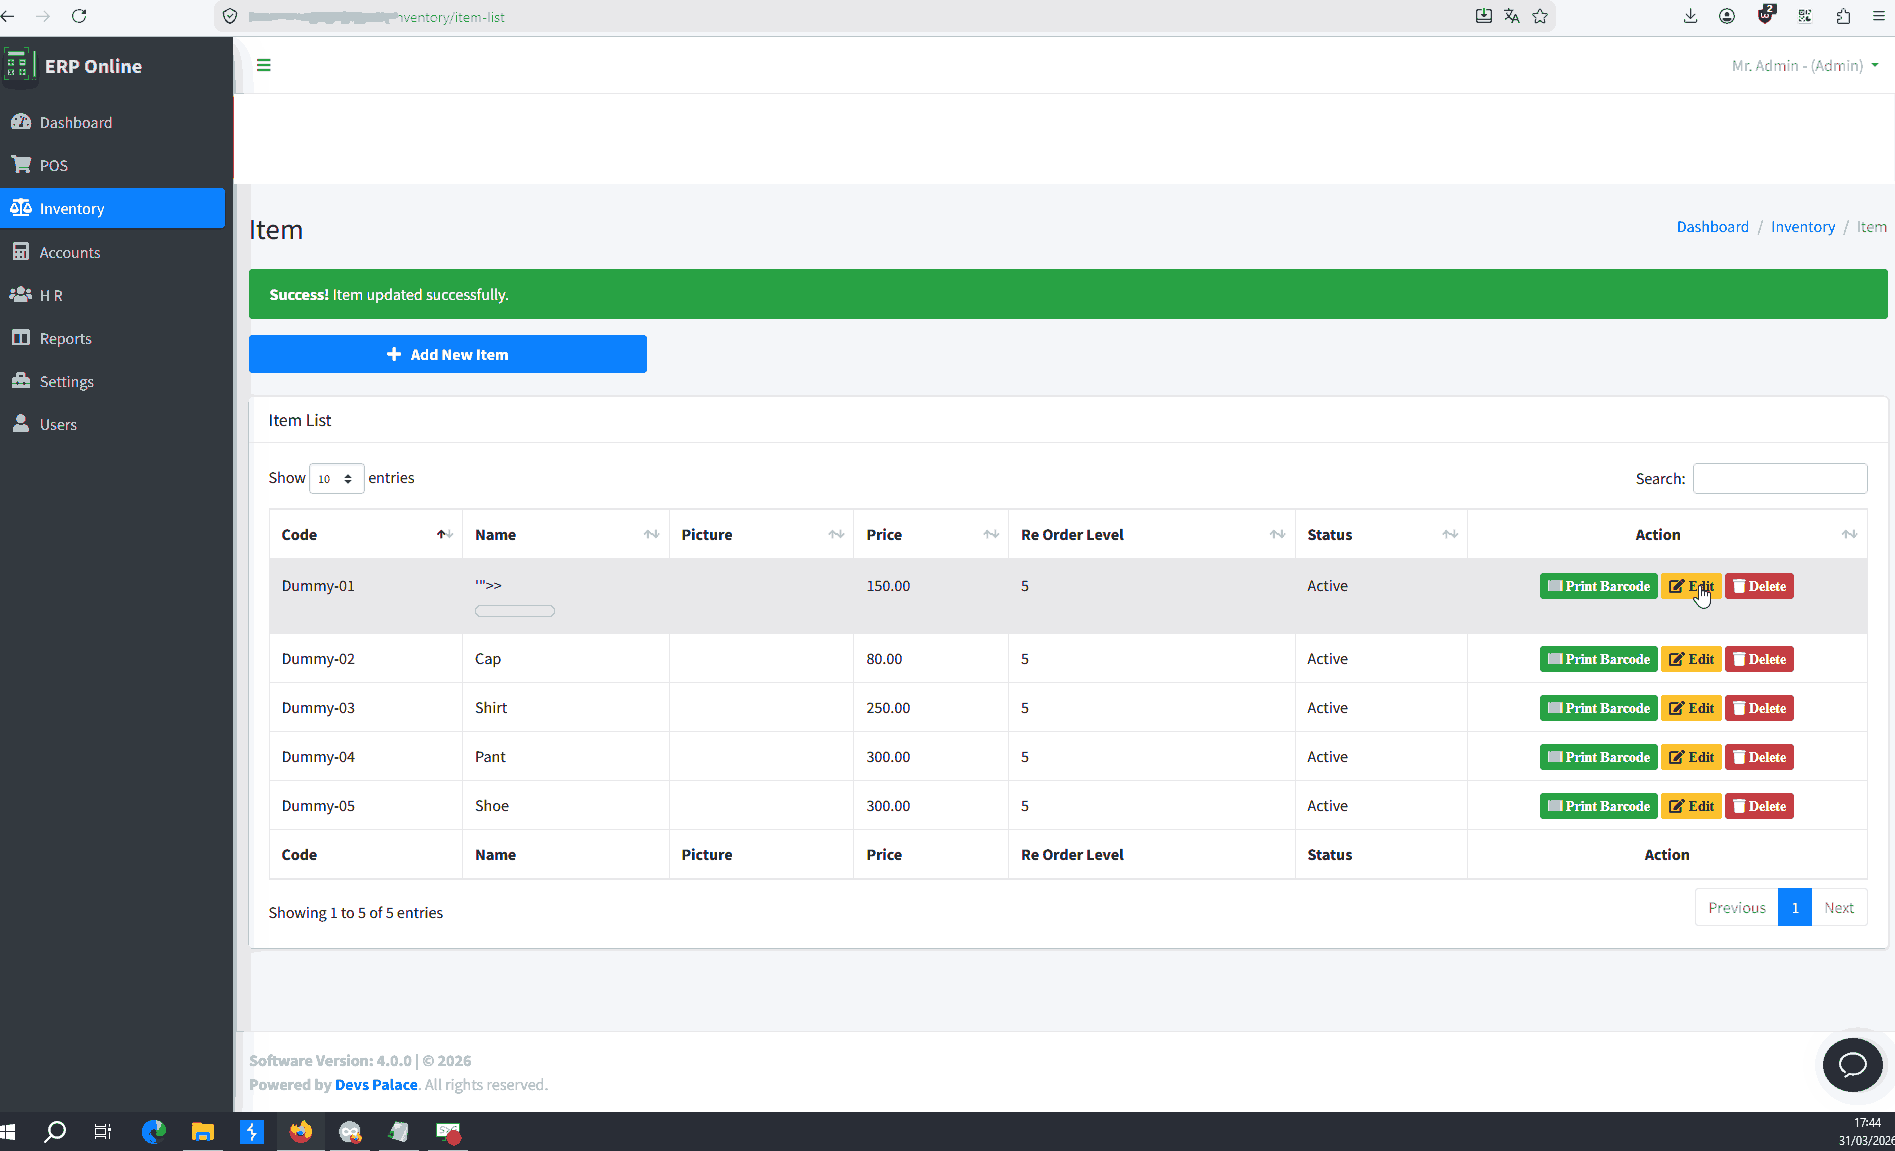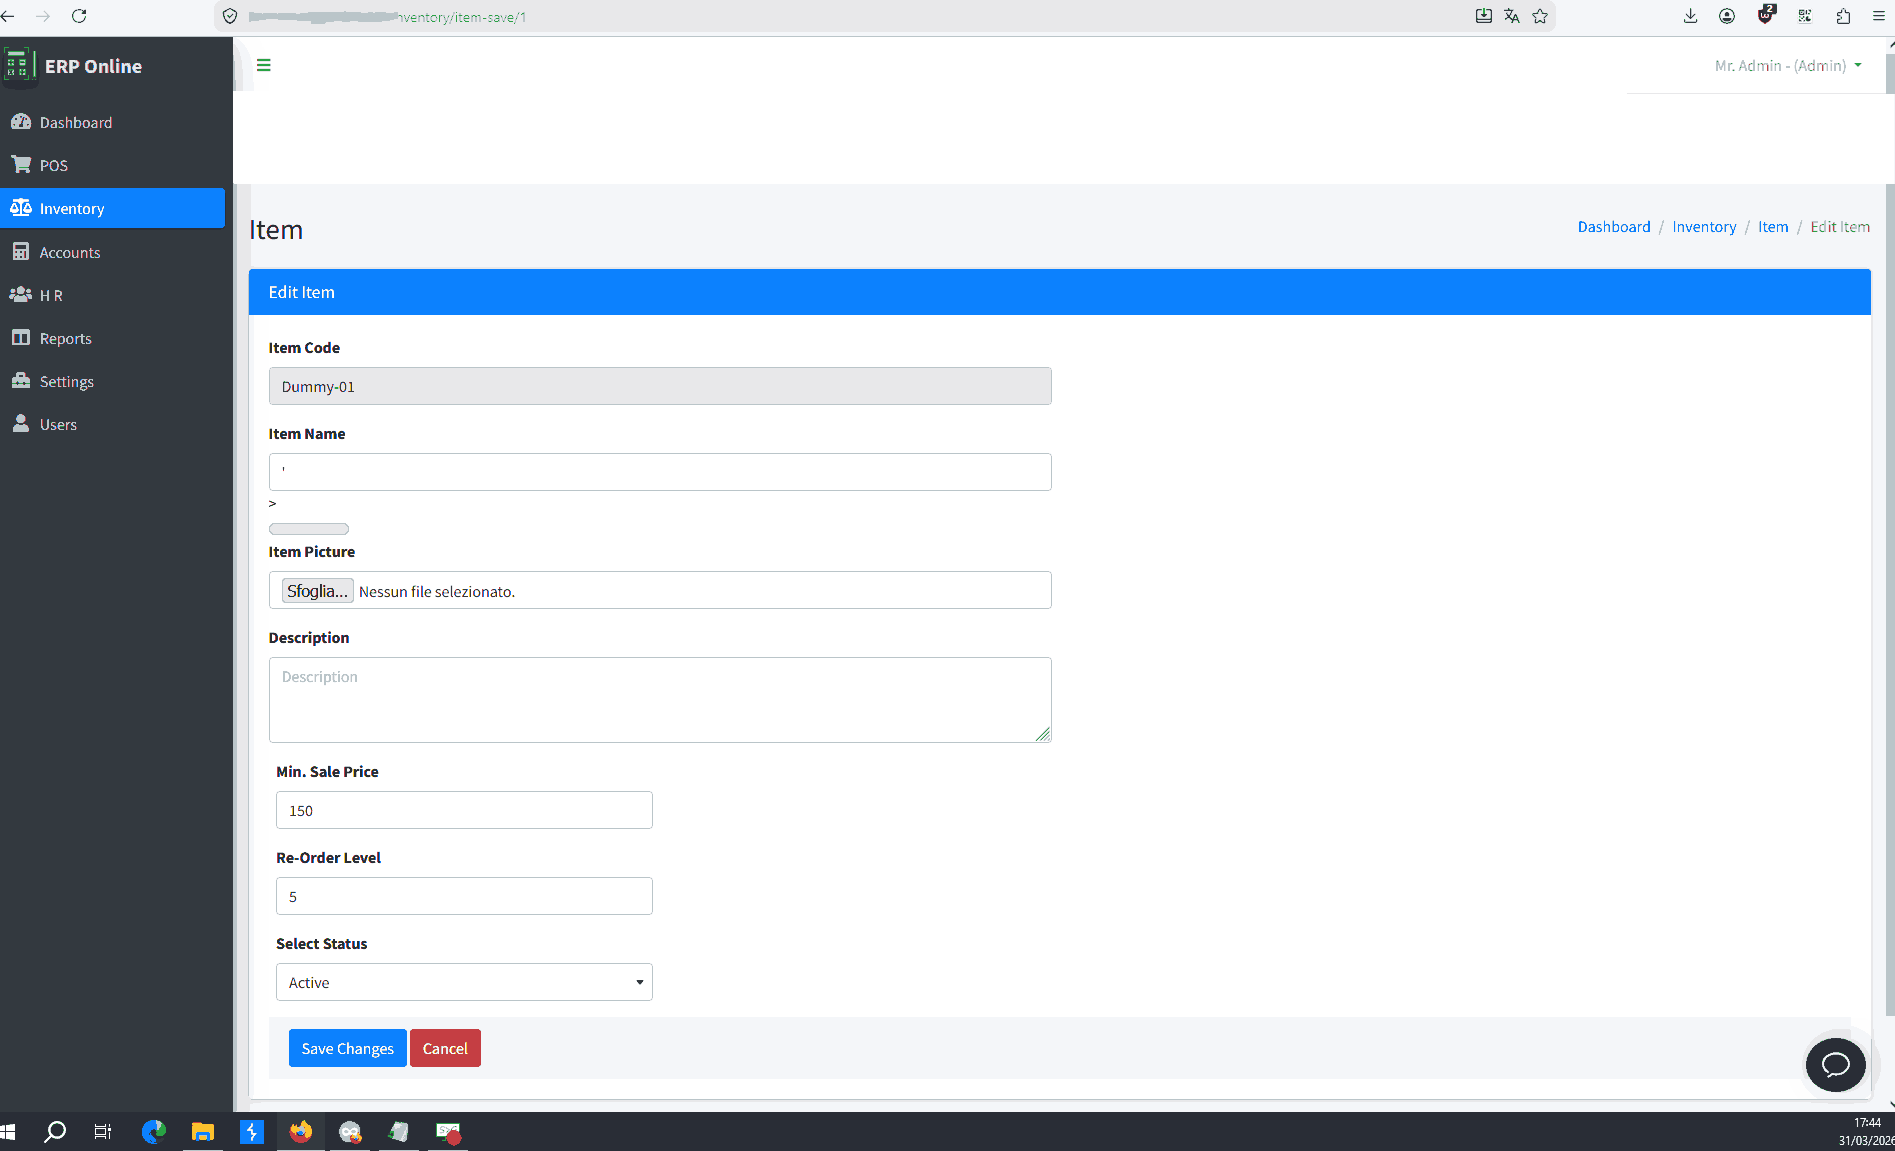
A flaw has been found in Devs Palace ERP Online up to 4.0.0. This impacts an unknown function of the file /inventory/item-save. This manipulation causes cross site scripting. The attack is possible to be carried out remotely. The exploit has been published and may be used. The vendor was contacted early about this disclosure but did not respond in any way.
מדדים
- CVSS 3.1
-
2.4 (LOW)
מקור הציון: CNA
CVSS:3.1/AV:N/AC:L/PR:H/UI:R/S:U/C:N/I:L/A:N - CVSS 4.0
-
1.9 (LOW)
מקור הציון: CNA
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X - EPSS — סבירות ניצול
- 0% (אחוזון 000) נכון ל-29/9/2026
- CWE
- CWE-79, CWE-94