CVE-2026-6743
נמוכה 3.5
תיאור (מקור, אנגלית)
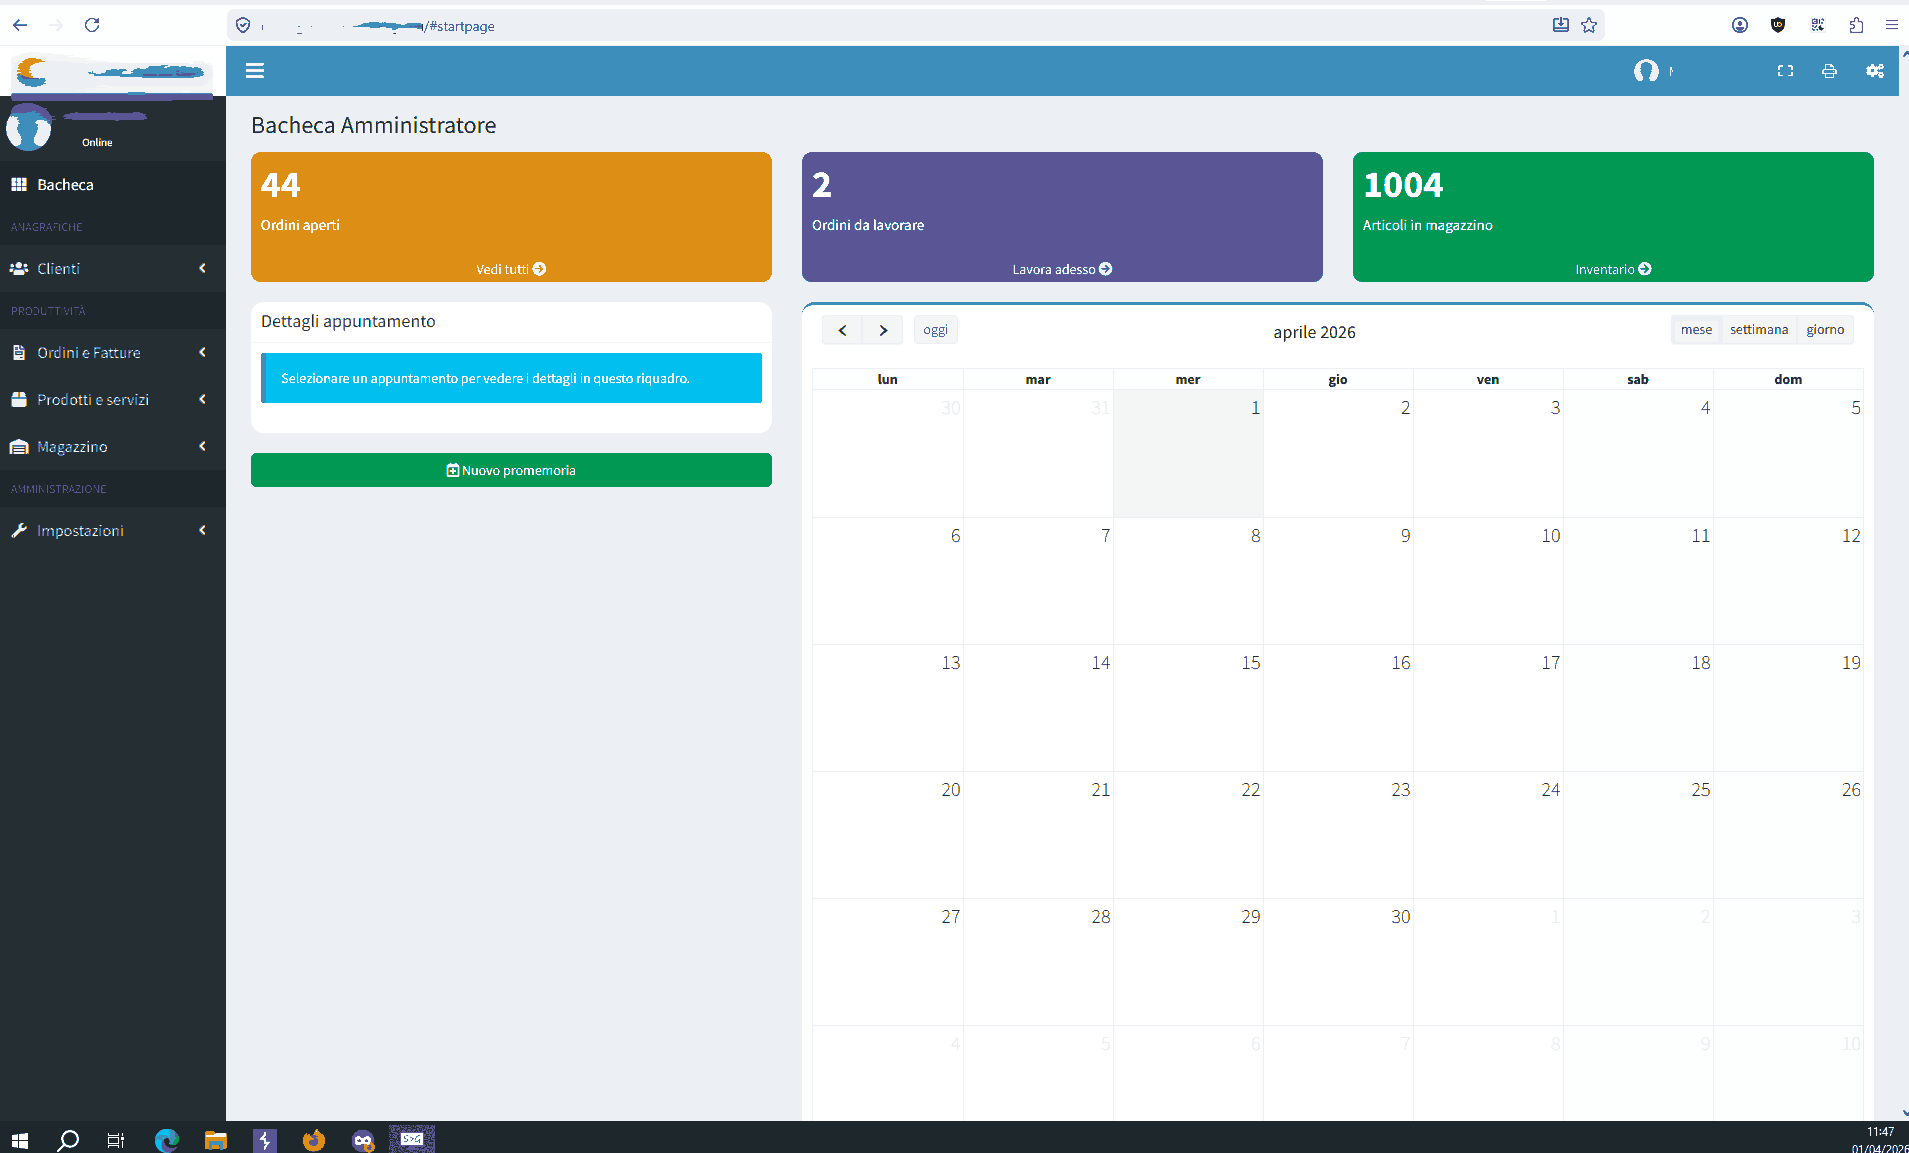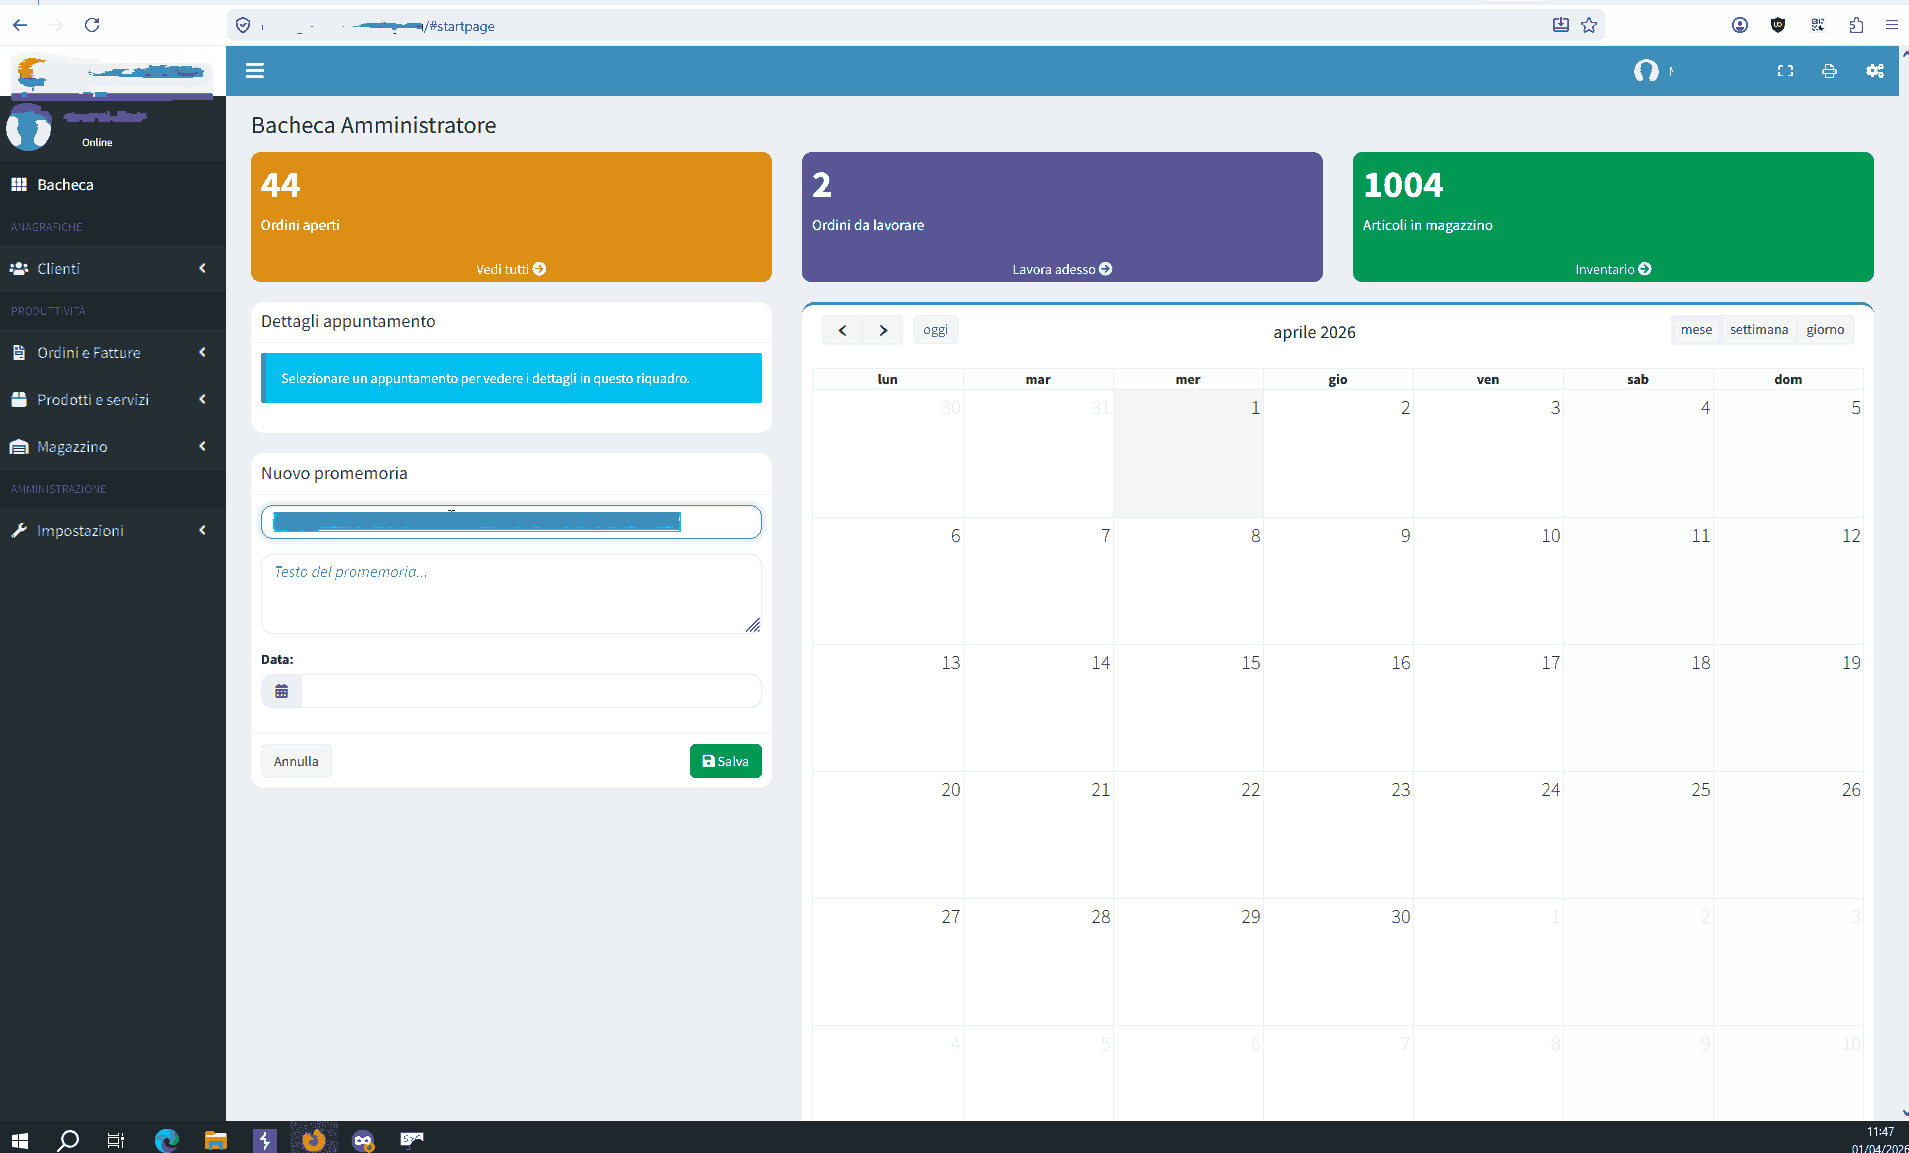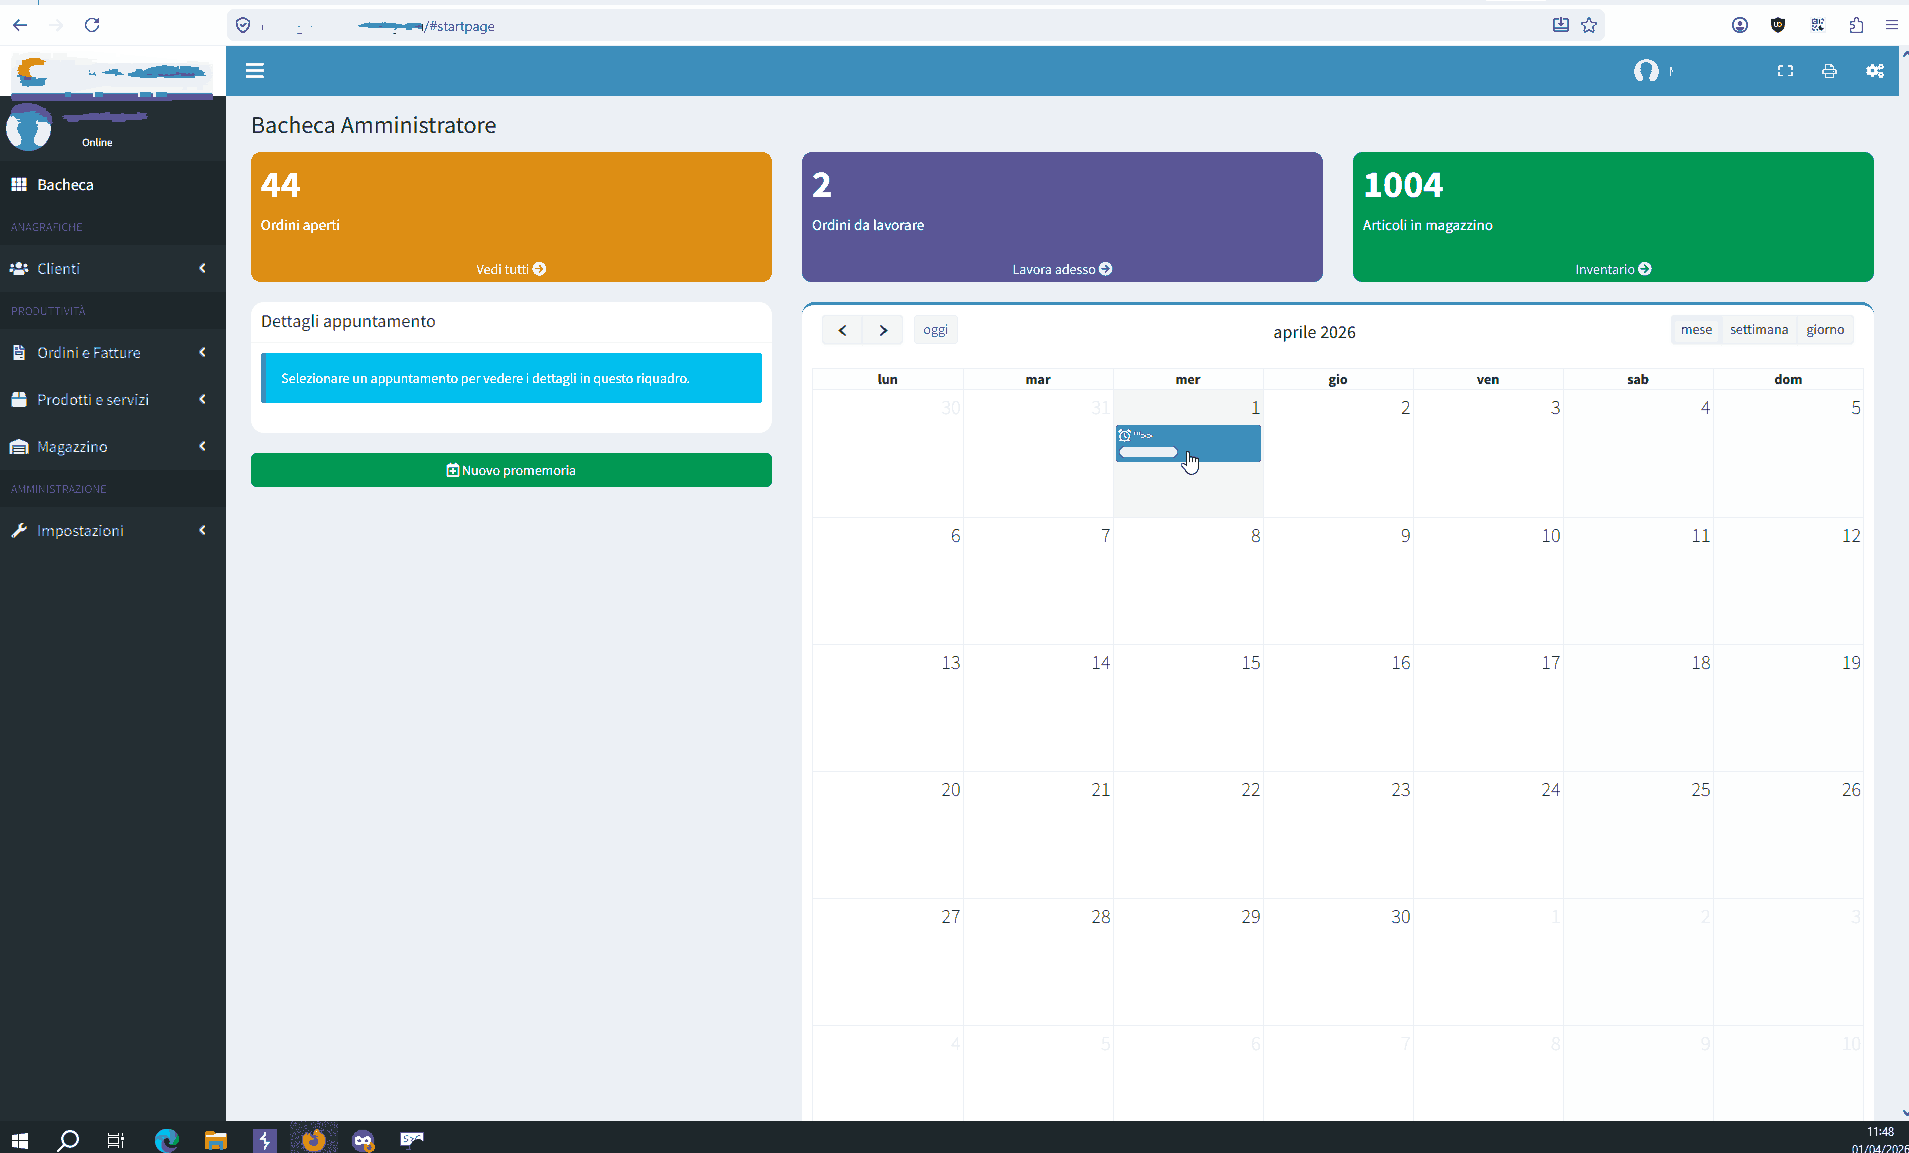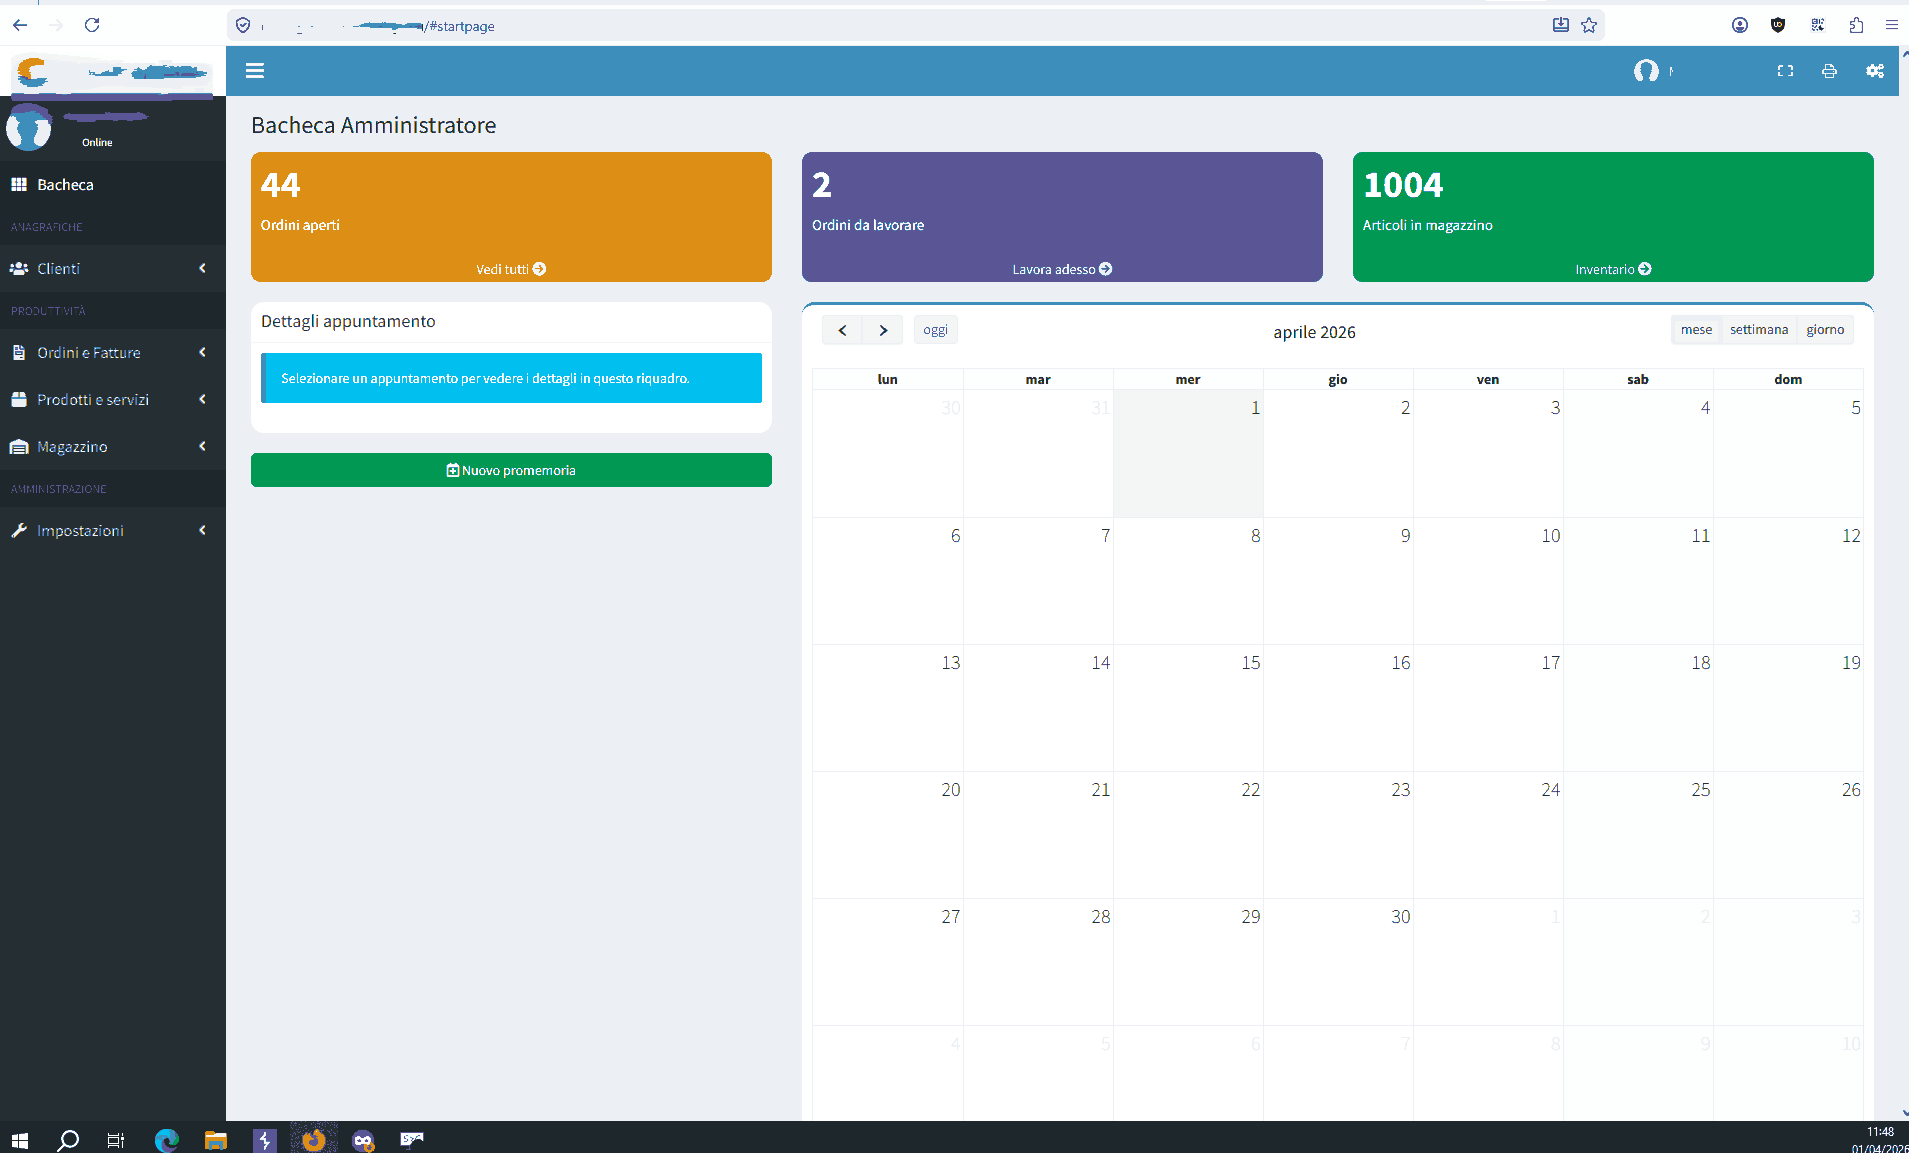
A vulnerability has been found in WebSystems WebTOTUM 2026. This impacts an unknown function of the component Calendar. The manipulation leads to cross site scripting. The attack may be initiated remotely. The exploit has been disclosed to the public and may be used. Upgrading the affected component is recommended. The vendor was contacted early, responded in a very professional manner and quickly released a fixed version of the affected product.
מדדים
- CVSS 3.1
-
3.5 (LOW)
מקור הציון: CNA
CVSS:3.1/AV:N/AC:L/PR:L/UI:R/S:U/C:N/I:L/A:N - CVSS 4.0
-
2.0 (LOW)
מקור הציון: CNA
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:P/VC:N/VI:L/VA:N/SC:N/SI:N/SA:N/E:P/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X - EPSS — סבירות ניצול
- 0% (אחוזון 000) נכון ל-25/9/2026
- CWE
- CWE-79, CWE-94